
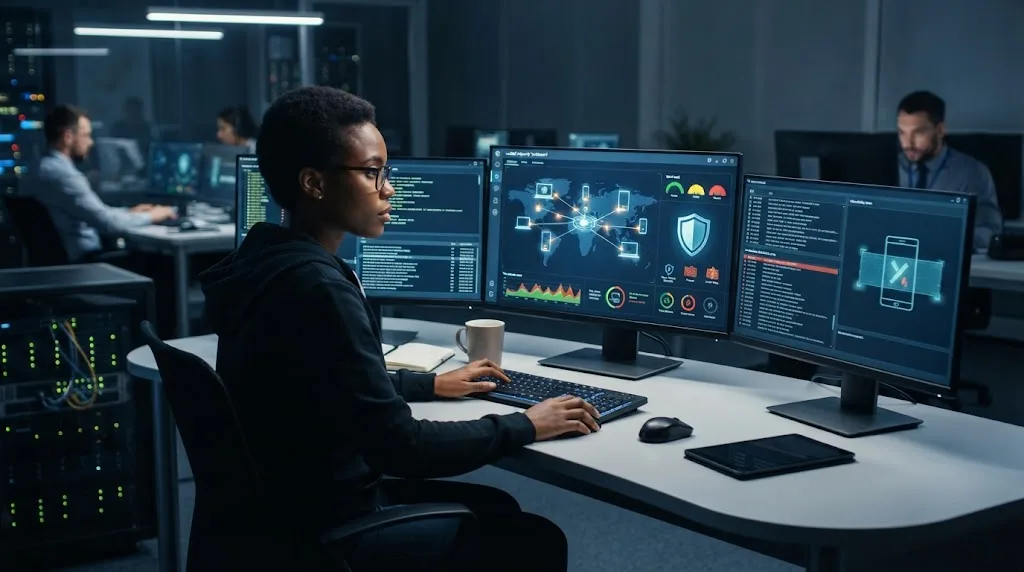
Endpoint security protects computers, laptops, smartphones, tablets, servers, and other devices that connect to a business network or cloud environment. These devices are often where employees access email, customer information, financial systems, and company files. If attackers compromise one endpoint, they may gain a starting point for stealing data or moving deeper into an organization.
Traditional antivirus remains useful, but modern endpoint protection goes much further than scanning files for known viruses. Security platforms can monitor applications, user behavior, network activity, suspicious processes, ransomware techniques, and other indicators of attack. This broader approach helps organizations identify threats that may not look like traditional malware at first.
Endpoint security matters even more as businesses adopt remote work, cloud services, mobile devices, and bring-your-own-device policies. Employees may connect from home networks, hotels, airports, and other locations outside the traditional office perimeter. Protecting individual devices therefore becomes an essential part of protecting the entire organization.
What Is Endpoint Security?
Endpoint security is the practice of protecting devices that connect to an organization’s network, applications, or data. An endpoint can include a desktop computer, laptop, smartphone, tablet, server, point-of-sale device, or other connected system. Security tools monitor these devices for malicious activity and help prevent unauthorized access, malware infections, and data theft.
Modern endpoint security platforms generally combine several protective capabilities rather than relying on one antivirus engine. These can include malware prevention, behavioral detection, firewall controls, device management, application monitoring, encryption, and threat response. Centralized management also allows IT teams to apply policies and review alerts across many devices from one security console.
The main objective is to reduce the risk that one compromised device becomes an entry point into a larger environment. Employees interact with files, websites, email attachments, cloud applications, and external devices every day. Endpoint protection adds security directly where these activities happen, making it an important defense against both common and advanced cyber threats.
Why Endpoint Security Matters for Businesses
Endpoints are attractive targets because they are used constantly and often contain direct access to valuable information. A successful phishing email could install malware on an employee laptop, while stolen credentials might allow attackers to access business applications. Once a device is compromised, criminals may attempt to steal files, capture passwords, or reach other internal systems.
Small and large businesses face similar endpoint risks, although their resources may differ. Ransomware, information-stealing malware, business email compromise, and credential theft can all begin with one vulnerable employee device. Strong endpoint security helps detect suspicious activity earlier and can reduce the time attackers have to establish deeper access.
Security also supports business continuity. Malware infections can interrupt employee productivity, damage files, and force companies to disconnect systems while investigating an incident. Preventing or containing threats quickly can reduce downtime, recovery costs, and disruption while helping protect customer information and the organization’s reputation.
Endpoint Security vs. Traditional Antivirus
Traditional antivirus software was originally designed mainly to identify known malicious files. It often relied heavily on signatures, which are recognizable patterns associated with previously discovered malware. This approach still has value, but attackers now use techniques that may avoid placing an obvious malicious file on the computer.
Endpoint security uses a broader set of controls. It may analyze behavior, monitor processes, examine suspicious scripts, detect unusual account activity, and identify signs of ransomware or credential theft. Instead of asking only whether a file matches known malware, modern tools can also ask whether a program is behaving in a way that appears dangerous.
Another major difference is centralized management. Businesses may need to protect hundreds or thousands of devices, making individual antivirus dashboards impractical. Endpoint security platforms allow administrators to apply policies, investigate alerts, isolate devices, and review threat information from one place rather than managing every employee computer separately.
How Endpoint Protection Works
Endpoint protection usually starts with a lightweight security agent installed on each managed device. This software monitors activities such as file execution, application behavior, network connections, system changes, and suspicious processes. Information can then be analyzed locally, in the cloud, or through a combination of both methods.
When suspicious behavior appears, the security platform may block the activity automatically. For example, it could stop a malicious program from encrypting files, prevent an unknown process from accessing credentials, or quarantine a harmful download. Depending on the platform, administrators may also receive detailed alerts that help them understand what happened.
Some systems can automatically isolate a compromised computer from the wider network while still allowing the security team to investigate it. This can reduce the chance that ransomware or another threat spreads to additional devices. Fast containment is especially valuable during active attacks where every additional minute may increase the potential damage.
Endpoint Detection and Response Explained
Endpoint Detection and Response, commonly called EDR, focuses on continuously monitoring endpoints and helping security teams investigate suspicious activity. EDR tools collect detailed information about processes, file changes, user activity, and other events. This historical visibility can help analysts understand how an attack started and what the attacker did afterward.
EDR differs from basic prevention because it assumes that some threats may eventually bypass initial defenses. Instead of relying entirely on blocking everything, the system helps identify unusual behavior that deserves investigation. Security teams can search across endpoint activity, trace suspicious processes, and determine whether several alerts are connected to the same incident.
Response features can also help contain confirmed threats. Administrators may terminate malicious processes, quarantine files, isolate endpoints, or collect forensic information without physically touching the affected computer. These capabilities are valuable for organizations with remote employees or multiple offices where immediate hands-on access to every endpoint is impossible.
Common Threats Endpoint Security Helps Prevent
Malware remains one of the most familiar endpoint threats. Viruses, Trojans, spyware, information stealers, and ransomware can all target user devices through phishing emails, malicious downloads, compromised websites, or vulnerable software. Endpoint protection attempts to identify and block these threats before they can cause significant harm.
Credential theft is another major concern. Attackers may use malicious software to capture passwords, browser data, authentication tokens, or other account information stored on an endpoint. Once credentials are stolen, criminals may access cloud applications and business systems even if the original malware infection is later removed.
Endpoints can also be targeted through software vulnerabilities and unauthorized applications. Attackers may exploit outdated programs, while employees may accidentally install unsafe tools that create additional exposure. Endpoint controls can support patching, application restrictions, device policies, and monitoring that reduce the number of opportunities attackers can exploit.
How AI Is Changing Endpoint Security
Modern endpoint security increasingly uses machine learning and automated analysis to identify suspicious behavior. Instead of depending entirely on known malware signatures, security systems can examine large numbers of events and look for patterns associated with malicious activity. This can improve detection when attackers use new or modified techniques.
Automation can also help security teams prioritize alerts. Large organizations may generate thousands of endpoint events every day, making manual review difficult. Intelligent systems can connect related signals, highlight unusual behavior, and help analysts focus on incidents that appear more serious instead of treating every security notification equally.
Understanding these technologies can also be useful for people building careers in cybersecurity, data, or automation. Those interested in the wider technical concepts behind intelligent systems can learn AI alongside security fundamentals. AI can support detection, but experienced human judgment remains important when investigating complex incidents and making response decisions.
Essential Endpoint Security Features to Look For
Real-time malware protection should be one of the basic features of any endpoint security platform. The system should monitor files and applications while they run rather than relying only on scheduled scans. Behavioral detection is also valuable because it can identify suspicious actions even when the exact malware has never been seen before.
Centralized management is particularly important for businesses. IT teams should be able to see device status, apply policies, review alerts, and respond to threats without visiting every computer individually. Features such as device isolation, application control, firewall management, and security reporting can make endpoint protection easier to operate across a growing organization.
Look for tools that fit the actual environment rather than choosing the product with the longest feature list. Consider Windows, macOS, Linux, mobile devices, remote employees, cloud applications, and existing IT systems. A security platform provides more value when the team can configure, monitor, and respond to alerts effectively without creating unnecessary complexity.
Best Practices for Stronger Endpoint Security
Keep every operating system and application updated. Security patches fix vulnerabilities that attackers may already know how to exploit, making patch management one of the simplest ways to reduce endpoint risk. Businesses should maintain visibility into outdated devices and replace systems that no longer receive vendor security support.
Use multi-factor authentication and strong unique passwords for important accounts. Endpoint security can stop many malicious programs, but stolen credentials may still allow attackers to access cloud services directly. Combining endpoint protection with identity security creates stronger defenses than relying on either technology alone.
Employees should also receive regular cybersecurity awareness training. Phishing emails, fake login pages, malicious attachments, and social engineering remain common ways attackers target endpoints. Teaching staff to verify unusual requests and report suspicious activity quickly can give security teams valuable time to investigate and contain potential threats.
Endpoint Security for Remote and Hybrid Work
Remote work has changed where endpoints connect from and how companies protect them. An employee laptop may move between the corporate office, a home network, a hotel, and public Wi-Fi within the same week. Security can no longer assume that every business device remains safely inside a traditional office network.
Cloud-managed endpoint platforms are useful because policies and threat monitoring can continue wherever the device has an internet connection. Businesses can apply security updates, review alerts, and investigate suspicious activity without requiring employees to return to the office. Device encryption and secure remote access provide additional protection when equipment leaves company premises.
Remote workers also need clear rules for personal devices and home networks. Businesses should define which devices can access sensitive information, what security software is required, and how lost or stolen devices should be reported. Consistent policies reduce confusion and help ensure remote work does not create unnecessary gaps in endpoint protection.
How Small Businesses Can Improve Endpoint Security
Small businesses should begin by identifying which devices access important company information. Create a simple inventory of laptops, desktops, smartphones, servers, and other business endpoints. Knowing what needs protection makes it easier to identify outdated systems, missing security software, and devices that should no longer have access.
Next, establish basic security controls across every business device. Enable automatic updates, use reputable endpoint or antivirus protection, turn on firewalls, encrypt sensitive devices, and require strong authentication. Businesses should also maintain secure backups so ransomware or hardware failures do not leave critical information permanently unavailable.
Finally, create a clear process for responding to suspicious activity. Employees should know whom to contact if they notice pop-ups, strange login alerts, unusual files, or unexpected security warnings. Fast reporting allows the responsible IT person or provider to isolate the device before one endpoint problem develops into a wider company incident.
Conclusion
Endpoint security protects the computers, phones, servers, and other devices that connect people to business information and applications. Modern protection goes beyond basic antivirus by combining malware prevention, behavioral analysis, device controls, centralized management, and response capabilities. These layers make it harder for attackers to turn one vulnerable endpoint into broader access.
Businesses should combine endpoint protection with software updates, strong authentication, employee training, backups, and sensible access controls. No single security platform can eliminate every risk. A layered approach reduces the chance that one phishing email, stolen password, outdated application, or malicious download creates a serious security incident.
As organizations continue adopting cloud services and flexible work arrangements, endpoint security will remain a critical part of cybersecurity. Devices are often where employees interact directly with sensitive information, making them natural targets for attackers. Protecting those endpoints consistently helps safeguard data, reduce downtime, and strengthen the overall security of the business.
FAQs
What is endpoint security in simple terms?
Endpoint security protects devices such as laptops, desktops, phones, and servers from cyber threats. It can detect malware, monitor suspicious behavior, enforce security policies, and help businesses respond when a device becomes compromised.
Is endpoint security the same as antivirus?
No. Antivirus mainly focuses on detecting malicious software, while modern endpoint security can also include behavioral monitoring, threat investigation, device control, network protection, centralized management, and automated incident response.
Why do small businesses need endpoint security?
Small businesses use devices to access customer information, payments, email, and cloud applications. Protecting those endpoints reduces the risk that malware, stolen credentials, or one compromised laptop disrupts the entire organization.
What is EDR in endpoint security?
EDR stands for Endpoint Detection and Response. It continuously monitors endpoint activity, helps security teams investigate suspicious behavior, and provides response capabilities such as isolating devices or stopping malicious processes.
Can endpoint security stop ransomware?
Endpoint security can detect and block many ransomware techniques, especially through real-time and behavioral monitoring. However, businesses should also maintain secure backups, patch software, use strong authentication, and train employees to reduce ransomware risk.